An it disaster recovery plan template for small business works when it records what you run, how fast each system must return, who acts, and where backups live. Fill it in before an outage, not during one.
Recovery planning is one layer of protection. It sits alongside the controls in our small business cybersecurity checklist, and this template covers the restoration side: what to do once something has already broken.
What the plan has to anticipate
A recovery plan is built around what you lose, not around the story of how you lost it. Ready.gov’s recovery plan guidance says data can be lost, corrupted, compromised or stolen through hardware failure, human error, hacking and malware. Ransomware falls under malware and hacking, so it needs no separate plan, only a recovery path that does not depend on the infected systems.
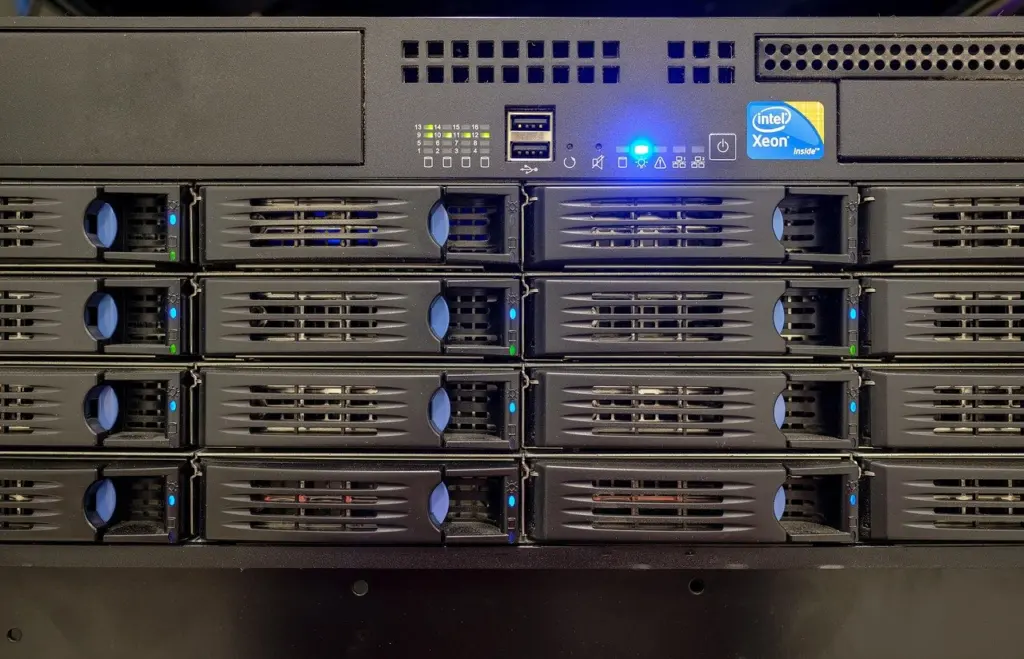
The same guidance says recovery strategies should anticipate the loss of one or more of these components:
- Computer room. The space that houses your servers or network gear may be unusable, so the plan needs an answer for where work happens meanwhile.
- Hardware. Servers, desktops, laptops and wireless devices can fail or disappear.
- Service connectivity. Systems may be intact but unreachable, which is a different problem from lost data.
- Software applications. Programs may need reinstalling or reconfiguring even when the data is safe.
- Data. Files and databases may need restoring from a backup copy.
The practical consequence is that each template section should answer a question about one of these losses. If a section does not help someone restore a component, it probably belongs in a different document.
A basic template also states its purpose plainly. The basic disaster recovery template at disasterrecoveryplantemplate.org lists goals of minimising interruptions, limiting damage and providing smooth, rapid restoration of service. Putting those goals at the top of your own plan gives anyone reading it under pressure a test for every decision.
Template sections at a glance
These are the sections a small business plan needs, in the order they are easiest to complete. Each later section depends on the one before it, so skipping ahead tends to leave gaps.
| Template section | What goes in it | Planning use |
|---|---|---|
| Inventory | Hardware (servers, desktops, laptops, wireless devices), software applications and data | Shows exactly what has to be restored, and gives every item someone to answer for it. |
| Business impact analysis | Critical processes, the impact if each is disrupted, and workarounds during restoration | Sets the restore order and tells staff how to keep working in the meantime. |
| Recovery time objectives | A recovery time for each IT resource that matches the business function depending on it | Gives a target to measure restore tests against. |
| Backup plan | Data identified, hardware and software selected, backups scheduled and conducted, and periodic validation | Defines what is copied, where, and how you know the copy works. |
| Testing | Periodic checks that the plan works | Finds broken assumptions before an incident does. |
The section contents follow Ready.gov’s recovery plan guidance and the University of Texas at Austin’s risk planning page.
Inventory and business impact analysis
Start with the inventory. Ready.gov describes the plan as beginning with a list of hardware, software applications and data, and that order is sensible: you cannot rank or restore what you have not written down. Record each item’s purpose alongside its name, because a list of model numbers does not tell a stand-in which system matters most.
Next comes the business impact analysis. The University of Texas at Austin describes it as identifying critical processes within an organisation and determining the impact if each process were disrupted, including workarounds to use while systems are being restored. For a small business, take that as a short table: the process, what stops when it stops, and what staff can do by hand or by another route in the meantime.
The university also notes that a business impact analysis needs participation from the management levels most familiar with how IT affects operations. In a small firm that usually means the owner or a department lead sits down with whoever manages the technology. An IT-only analysis tends to rank systems by technical convenience rather than by what the business cannot do without.
Recovery time objectives and recovery points
A recovery time objective, or RTO, is the target time to bring a function back. Ready.gov’s rule is that the recovery time for an IT resource should match the RTO of the business function that depends on it. A system cannot be allowed to return later than the process it supports can wait, and it gains nothing from being restored far faster than that process needs.
The practical effect is that RTOs cascade. If invoicing is critical, the accounting system, the database behind it and the network access to it all inherit that urgency. Write the target next to each item in your inventory rather than in a separate document, so the dependency is visible when someone is deciding what to restore next.
The companion measure is the recovery point objective, or RPO: how much recent work the business can afford to lose. It is what turns a vague promise to back up often into a schedule, and it is the reason the backup section of the template has to be written after the business impact analysis rather than before it.
RTOs are only a promise until they are checked. Ready.gov says data restoration times should be confirmed and compared with the IT and business function recovery time objectives. If a test restore takes longer than the target, change something: the backup method, the hardware, or the target itself, with the business owner’s agreement.
Backups that the plan can rely on
Ready.gov’s backup strategy has a clear sequence: identify the data to protect, select hardware and software, schedule and conduct backups, and periodically validate that the data has been accurately backed up. The last step is the one small businesses skip, and it is the one that tells you whether the rest worked.
The plan should also cover devices that hold data outside the server room. Ready.gov says the backup plan should include regularly scheduled backups from wireless devices, laptops and desktops to a network server. List those endpoints in the template so nothing stays only on a single laptop.
Backups only help if the plan says where they are and how to use them. Record the storage location, the person who can access it and the restore procedure for each data set. Keep that record in the same place as the rest of the plan so a responder does not have to hunt for it.
Roles, responsibilities and emergency contacts
The question of who does what during an incident is answered in writing, in advance. Name an incident lead who makes decisions, a technical lead who restores systems, and a communications lead who handles customers and staff. In a very small business one person may hold several roles, but the template should still show who covers each when someone is unavailable.
For each role, state what the person may decide without asking anyone: for example, approving a switch to another site or an urgent purchase. Decision authority is the gap that most often slows a response, so put it in plain words.
The contact list is the most-used page of the template. Purdue Global’s small business disaster recovery template includes these entries, which cover what most small firms need:
- Key personnel. Everyone with a role in the plan, with more than one way to reach them.
- Insurance. Policy details and the claims contact.
- Vendors. Computer hardware suppliers and other trades you would need to call.
- Customers and the bank. The contacts you would need to notify or approach.
- Offsite storage location. Where copies of data and the plan itself are kept.
If your team logs problems in a ticketing tool, the plan can point to it as the place to record the incident. Our guide to Best IT Help Desk Software For Small Business: Choose, Deploy, And Save Time In 2026 – Cubeguard covers what such tools do. Do not make the plan depend on one, because a help desk system may be among the services that are down.
Running the plan during an incident
At incident time the template should work as a short sequence a tired person can follow. The steps below are drawn from the sections above, in the order they are used.
- Confirm who is in charge. Open the contact and role pages, name the incident lead, and reach the technical and communications leads.
- Identify what was lost. Match the problem to a component from the list of computer room, hardware, connectivity, applications or data.
- Check the priority. Look up the affected systems in the inventory, with their business impact notes and recovery time objectives.
- Restore from the backup record. Use the stored location and procedure for the data set, and use the documented workarounds while it runs.
- Compare against the target. Note how long restoration took against the recovery time objective, so the plan can be corrected afterwards.
Some recoveries need outside help, such as a hardware supplier or an IT provider. Deciding in advance whether to retain one is a budget question, and How Much Does IT Support Cost For Small Businesses In 2026? A Practical Pricing Guide – Cubeguard sets out what that support can cost so you can weigh it before you need it.
Testing and keeping the plan current
Ready.gov’s instruction is to test the plan periodically to make sure it works. It does not set an interval, so choose one that suits how quickly your systems and staff change, and write the date of the last test into the document. A restore test is the most informative, because it checks both the backup and the stated recovery time in one step.
Treat each test as a source of corrections. If a contact no longer answers, a backup location has moved or a system is missing from the inventory, update the template the same day. Contacts and vendors change whenever staff or suppliers change, so revisit those pages whenever that happens rather than waiting for the next scheduled test.
For deeper reference, Ready.gov lists NIST Special Publication 800-34 Rev. 1, the Contingency Planning Guide for Federal Information Systems. It is written for federal systems, so use it as a source of ideas and structure rather than as a requirement for a small business.
Frequently asked questions
How often should backups run?
Ready.gov says data should be backed up frequently but gives no fixed interval. Choose a schedule from how much recent work you could afford to lose, and have the plan include regularly scheduled backups from laptops, desktops and wireless devices to a network server.
Where should the plan itself be kept?
Keep a copy in a safe, accessible off-site location, as the basic template at disasterrecoveryplantemplate.org advises. A plan stored only on the server it describes is unreachable when that server fails.
What about paper records?
Ready.gov says hard copy vital records can be backed up by scanning paper records into digital formats. Once scanned, they can join the same backup schedule as the rest of your data.
Is there a ready-made template I can download?
The University of Texas at Austin’s risk planning page offers a Disaster Preparedness Plan template that can be downloaded as a Word document. Adapt it to your own inventory, roles and contacts rather than using it unchanged.